
FADP & GDPR Compliance: The Complete Guide for Swiss & European Businesses in 2026
The practical guide to making your website compliant without losing your marketing data. FADP or GDPR, real penalties, a cookie banner that works, Consent Mode v2 and a strategy for your company size, with an 8-question checklist.
Table of content
1. Compliance has become a marketing issue
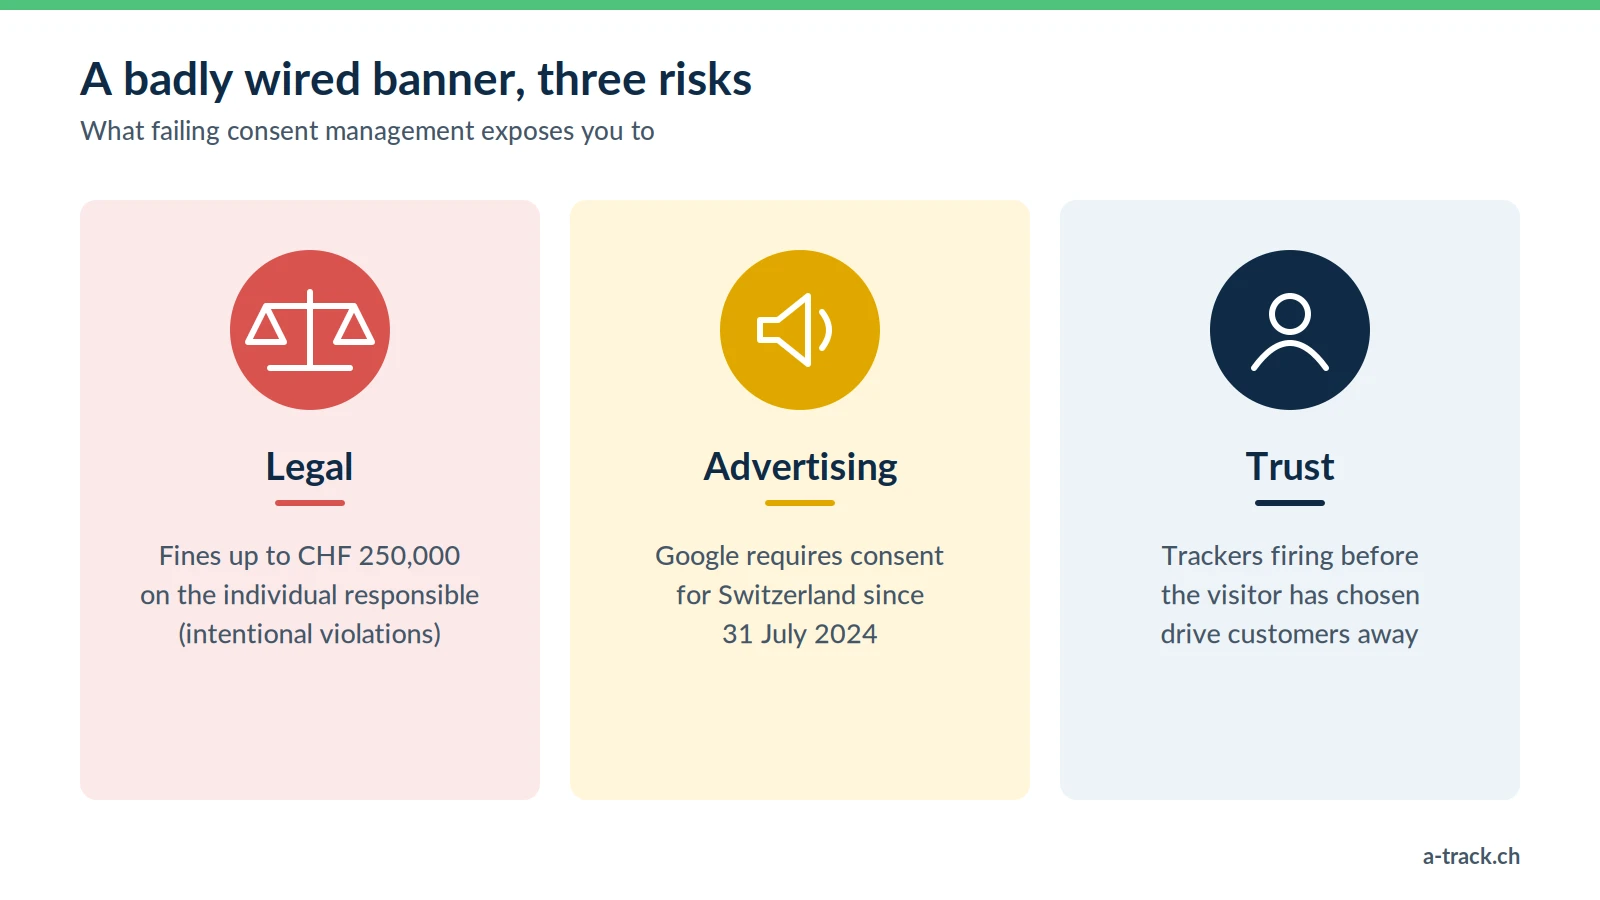
For a long time, the cookie banner was seen as a legal formality. Not anymore: a badly wired banner exposes a company to three risks at once.
Legal risk: the FADP provides for fines of up to CHF 250,000, imposed on the individuals responsible.
Advertising risk: since 31 July 2024, Google has applied its consent policy to Swiss visitors. Without consent signals, remarketing and conversion measurement deteriorate.
Trust risk: a visitor who sees trackers firing before they have made a choice does not come back.
At A-Track, we handle these three risks together: what is legally right must also work technically.
2. FADP or GDPR: which law applies to your website?
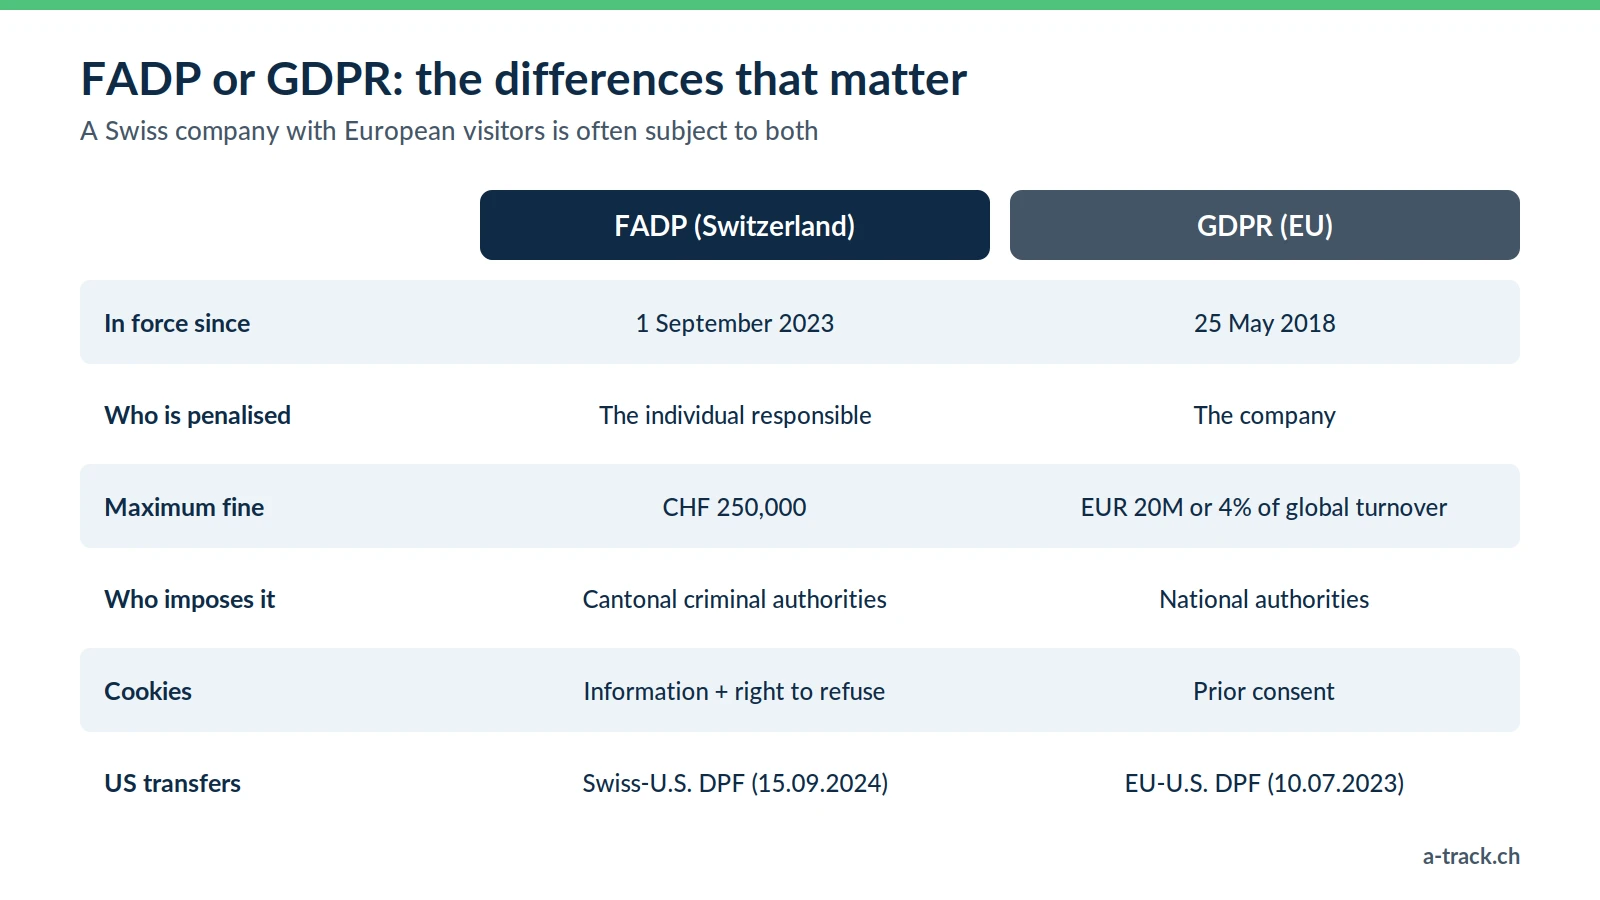
Often both. The revised FADP has been in force since 1 September 2023. The GDPR also applies to a Swiss company as soon as it offers goods or services to people in the European Union, or monitors their behaviour online (Article 3 GDPR).
Who is penalised? The FADP mainly targets the individuals responsible, and only for intentional violations (Art. 60 to 63 FADP). The GDPR targets the company, up to EUR 20 million or 4% of worldwide turnover.
Cookies: in Switzerland, the Telecommunications Act (Art. 45c TCA) requires you to inform visitors and let them refuse. In the EU, prior consent is required for any non-essential tracker. As soon as you have European visitors or use Google Ads, aim for the stricter standard.
Transfers to the United States: they are possible to companies certified under the Swiss-U.S. Data Privacy Framework, in force since 15 September 2024. They must be documented in your privacy policy.
3. From complaint to penalty: how it works
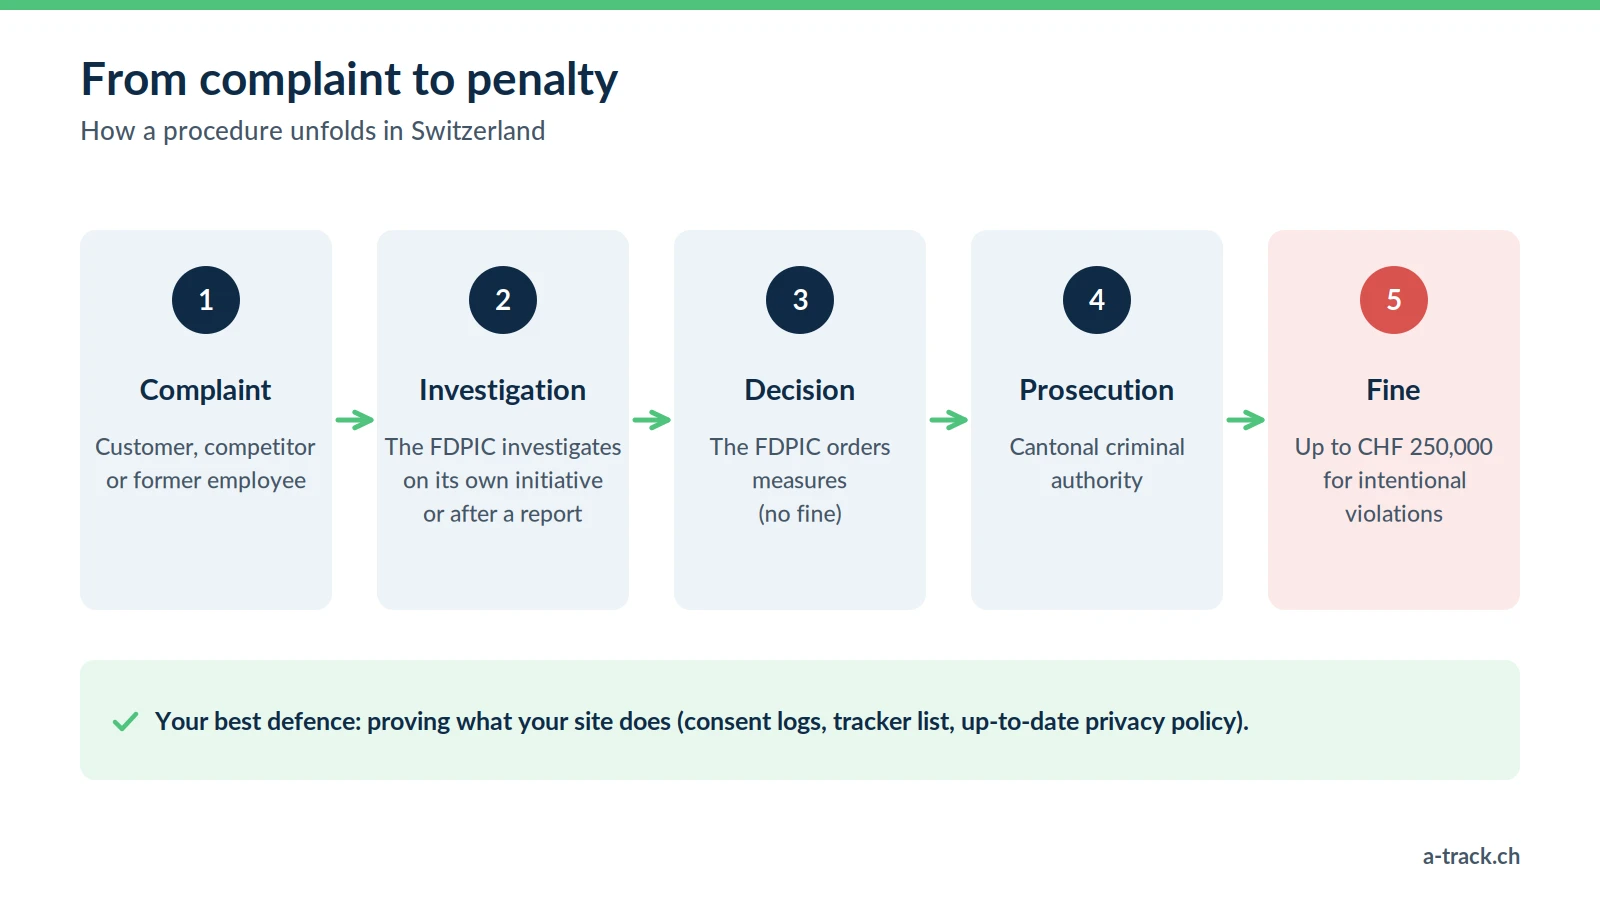
The Federal Data Protection and Information Commissioner (FDPIC) can open an investigation on its own initiative or following a report, for example after a complaint from a customer or a competitor. It can order measures, but it does not impose fines itself.
Fines are a matter for the cantonal criminal authorities. They cover in particular intentional breaches of information duties, failure to comply with an FDPIC decision and breaches of the duty of care. If the fine does not exceed CHF 50,000 and identifying the individual responsible would be disproportionate, the company can be fined instead (Art. 64 FADP).
Key point: your best protection is being able to prove what your website does. Consent logs, an up-to-date tracker list and a privacy policy that matches the technical reality.
4. The cookie banner that actually works
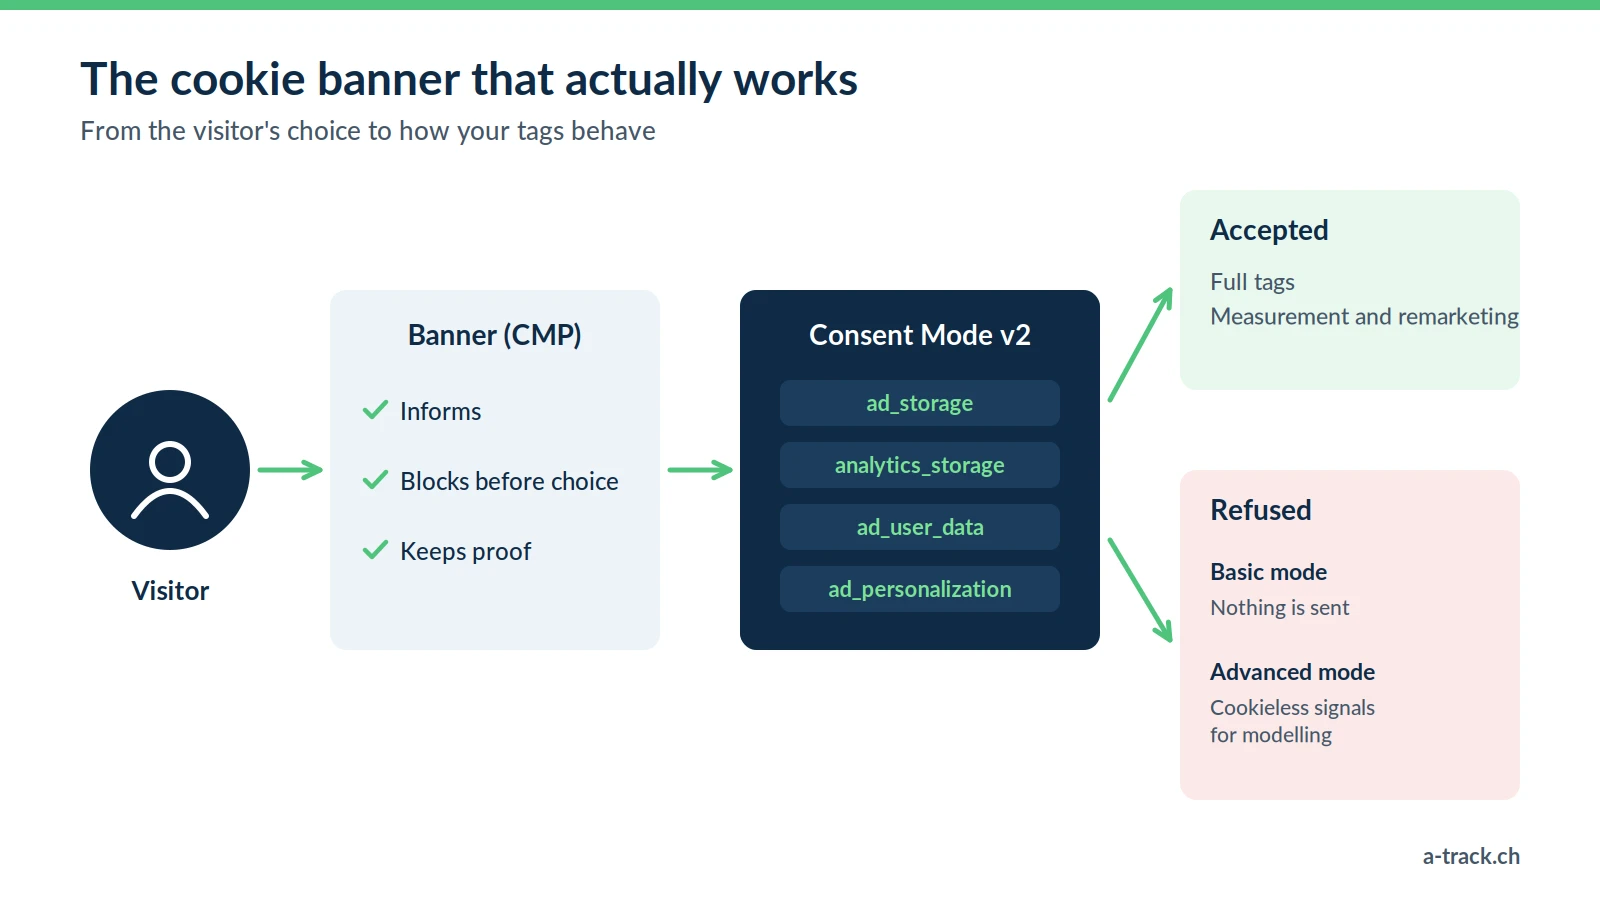
A banner that is displayed but blocks nothing is decorative. A CMP (Consent Management Platform) must do three things: inform, block trackers until the visitor has chosen, and keep proof of that choice.
Google Consent Mode v2 links that choice to your Google tags through four signals: ad_storage, analytics_storage, ad_user_data and ad_personalization.
Basic mode: Google tags only load after acceptance. Nothing is sent after a refusal.
Advanced mode: after a refusal, tags send cookieless signals that let Google model part of the conversions. According to Google, this modelling recovers more than 70% of the ad-click-to-conversion journeys lost to consent choices.
In both cases, the visitor's choice is respected. The difference is the quality of measurement, and it must be explained in your privacy policy.
5. Which strategy for your company size?
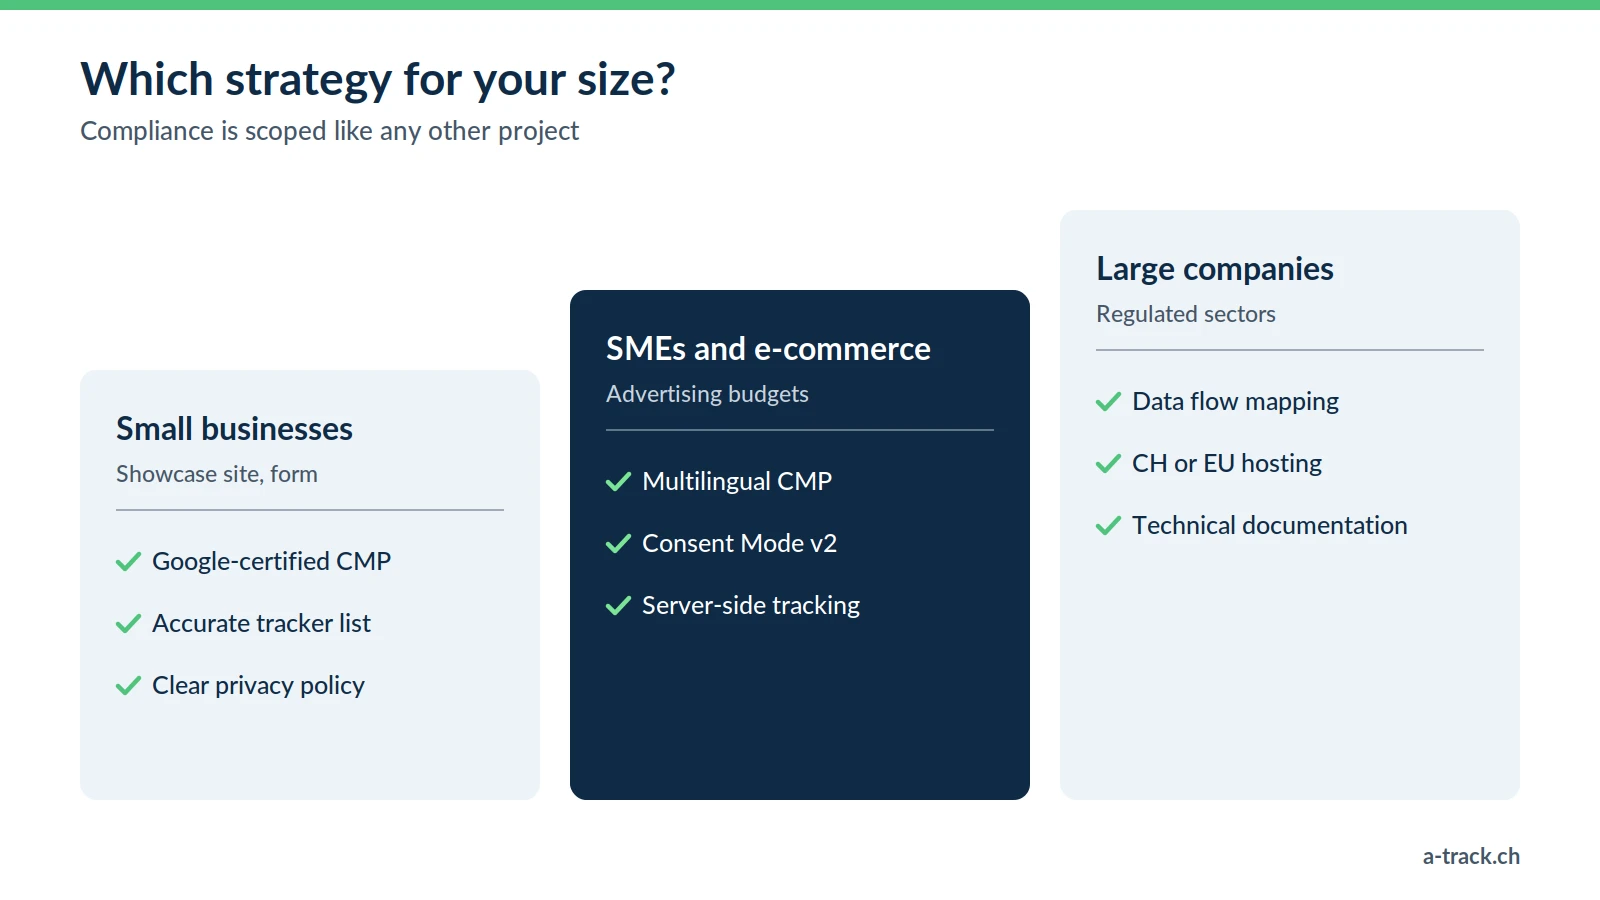
Small businesses and freelancers
A showcase site, a form, few tools. The essentials: a Google-certified CMP, an accurate tracker list and a clear privacy policy.
SMEs and e-commerce
You invest in advertising and your decisions depend on the numbers. You need a multilingual CMP, properly configured Consent Mode v2, regular tracker checks and, often, server-side tracking to make conversions reliable.
Large companies and regulated sectors
Finance, healthcare, industry: several domains, compliance teams and sensitive data. You need to map data flows, control recipients, choose where data is hosted (Switzerland or EU) and provide technical documentation your data protection officer can actually use.
6. The 5 steps to compliance with A-Track
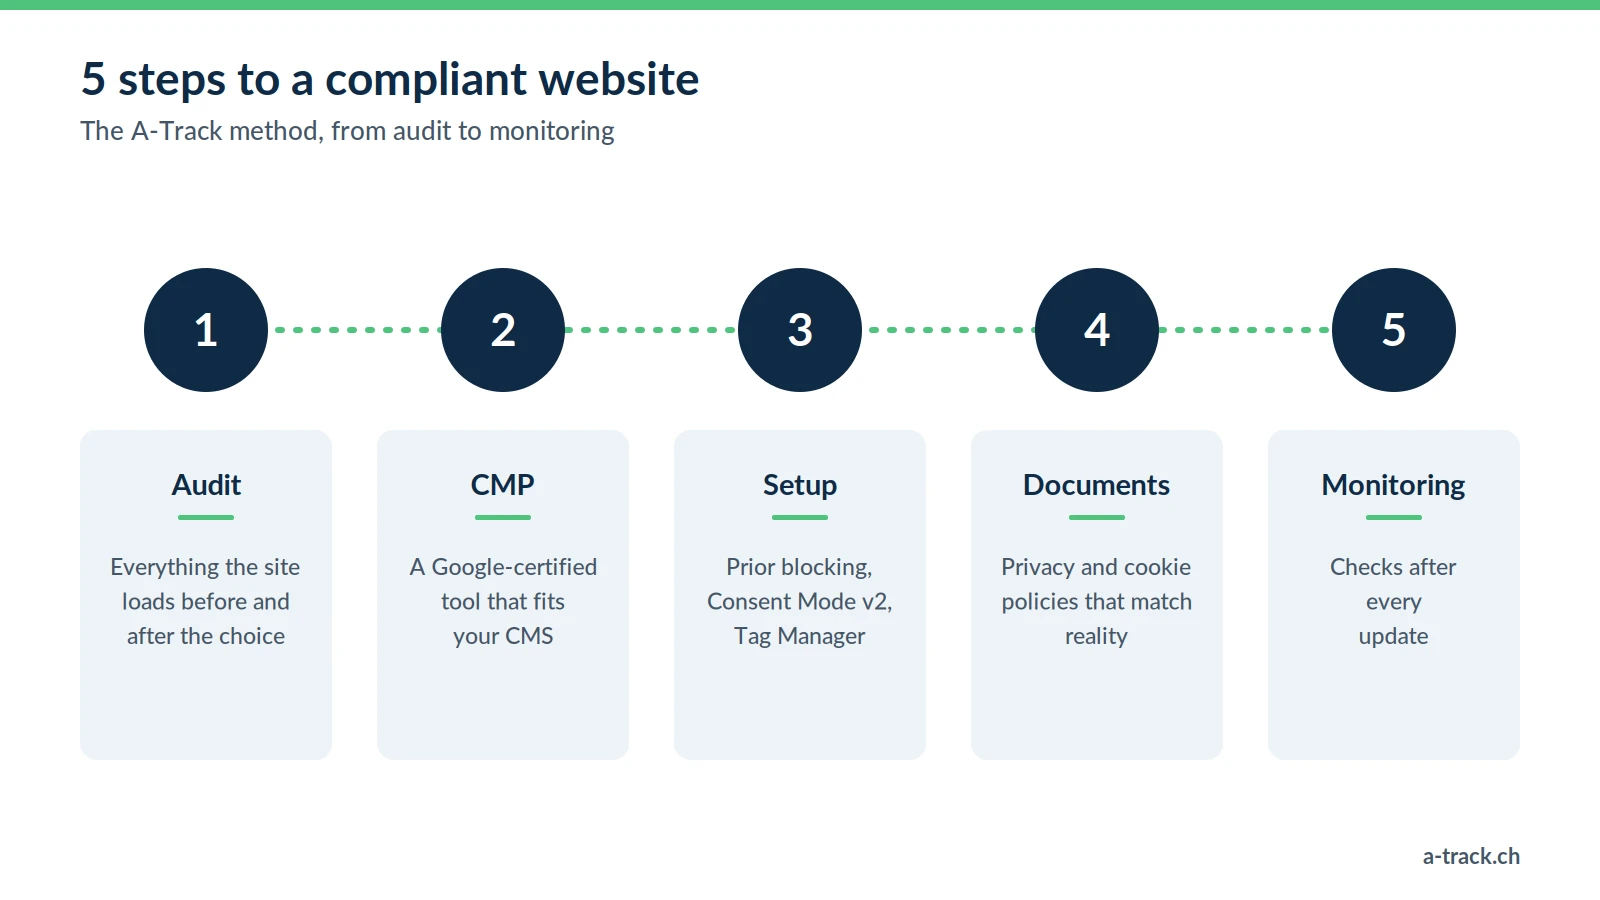
Audit: we record everything your site loads before and after the visitor's choice.
CMP selection: a Google-certified tool that fits your CMS, languages and budget.
Technical setup: prior blocking, Consent Mode v2 and Google Tag Manager.
Documents: privacy and cookie policies aligned with what actually runs.
Monitoring: regular checks, because one new plugin or update is enough to undo everything.
7. Is your website compliant? 8 questions to ask yourself
Do advertising trackers load before the visitor has chosen?
Is the "Reject" button as visible as the "Accept" button?
Is your CMP on Google's list of certified CMPs?
Does Consent Mode v2 send all four signals?
Do you keep proof of consent?
Does your privacy policy list every provider actually present on the site?
Do you know which countries your data goes to?
Does anyone check the site after every update?
A single uncertain answer is enough to justify a check. Request your free audit within 48 hours, or see our services and prices. For the impact on marketing measurement, read our Performance marketing and tracking guide.
Questions fréquemment posées
What is the "Privacy by Design" imposed by the FADP?
▾
What is the major difference between the FADP (Switzerland) and the GDPR (EU) for a website?
▾
What is the added value of a Swiss expert for the FADP?
▾
What are the financial risks in case of non-compliance with the FADP?
▾
These fines are imposed by cantonal criminal authorities; the FDPIC investigates and orders measures but does not impose fines. Indirect costs come on top: rushed remediation, reputational damage, limited advertising features.
Is the Meta Pixel compliant with the FADP in Switzerland?
▾
In practice, the simplest approach is to fire the Pixel only after consent, through your CMP. Server-side tracking lets you control and limit the data sent to Meta, but it does not replace consent: a refusal is still a refusal.
Is data compliance a hindrance to marketing performance?
▾
Is a CMP enough to be compliant?
▾
What documents does the FDPIC request during an FADP audit?
▾
1) The record of processing activities (Art. 12 FADP), from which companies with fewer than 250 employees are partly exempt.
2) Proof of consent choices, where you rely on consent (EU visitors, Google's policy).
3) The safeguards for data transfers outside Switzerland (Art. 16 FADP, for example the Swiss-U.S. DPF or standard clauses) and, if the processing is high-risk, an impact assessment (Art. 22 FADP).
4) Technical proof that non-essential trackers respect the visitor's choice (data protection by design and by default, Art. 7 FADP).
5) The processing agreements with your service providers (Art. 9 FADP).