Tracking & Compliance Audits
The problem: your tools report different numbers, tags fire before consent and nobody knows any more who installed what.
Our audits: tracking audit (client-side, server-side, server-to-server), FADP and GDPR compliance audit, data governance audit.
Your benefit: accurate data, a compliant website and a prioritised remediation plan shared with your teams and service providers.
Pricing: free flash audit within 48 hours, then full audits on a custom quote.
Table of content
GDPR, FADP and tracking audit: know what your tools really measure
Your conversion numbers differ from one tool to the next, tags fire before consent and nobody knows any more who installed what in Google Tag Manager. An A-Track audit answers three questions: is your data accurate, is it lawful, and who controls it?
We audit websites, apps and tracking servers for SMEs, web and marketing agencies and large organisations in Switzerland and across Europe. Three audit families, to combine according to your needs:
Tracking audit: client-side, server-side and server-to-server
FADP and GDPR compliance audit: Swiss and European law
Data governance audit: data flows, tools, access and documentation
1. Tracking audit
A tracking audit checks that every visit, lead and sale is measured once, in the right place and with the right value. We inspect your setup under real conditions, in all three consent states: refused, accepted and no choice made.
Client-side tracking audit
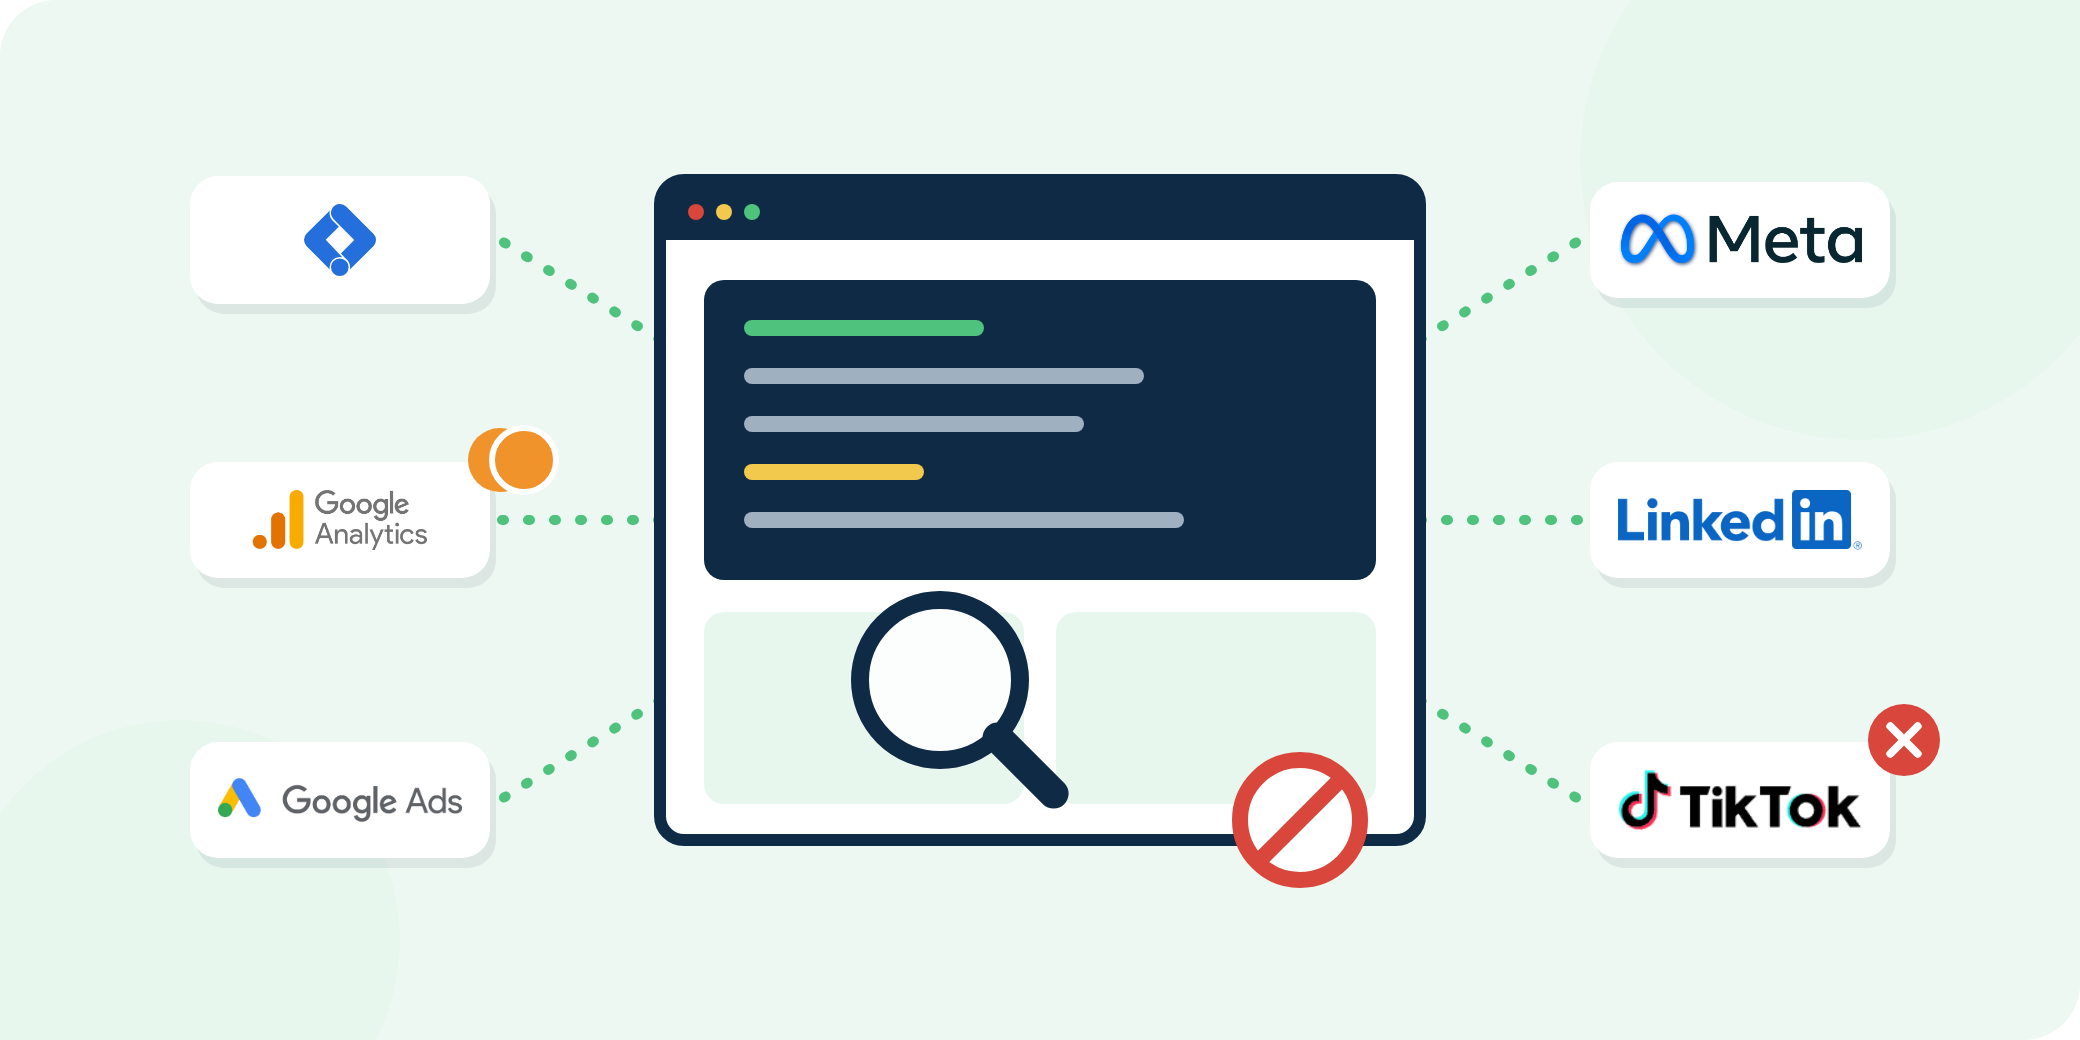
Inventory of tags and pixels: Google Tag Manager, GA4, Google Ads, Meta, LinkedIn, TikTok and others
Tagging plan, dataLayer and conversion events: duplicates, losses and wrong values
Impact of ad blockers, Apple ITP and private browsers on your data
Discrepancies between GA4, ad platforms, your back office and your CRM
Server-side tracking audit
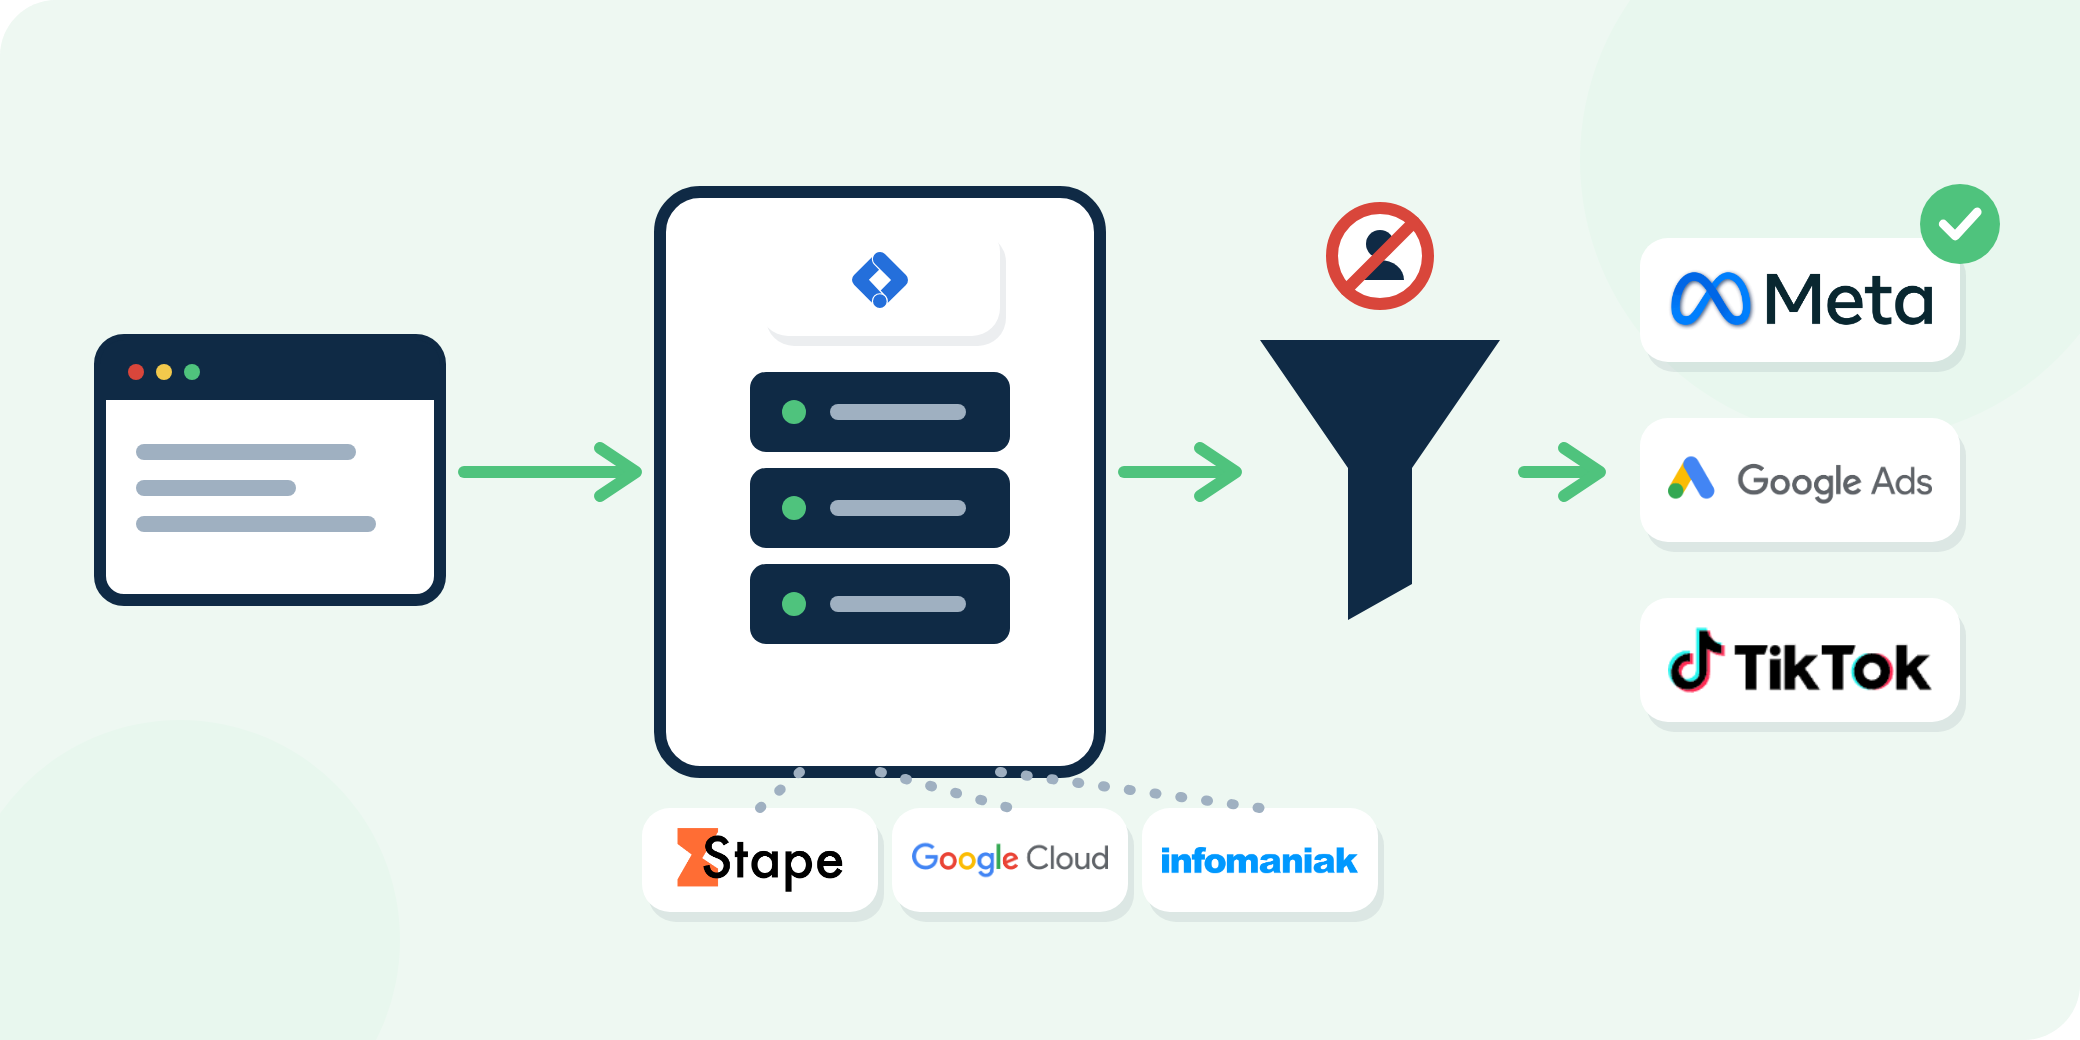
Server-side Google Tag Manager container (sGTM): clients, tags, transformations
First-party subdomain, hosting (Stape, Google Cloud, Infomaniak) and data location
Filtering of IP addresses and personal data before anything is sent to third parties
Conversion APIs (Meta CAPI, Google Ads enhanced conversions, TikTok Events API) and deduplication
Server-to-server tracking audit
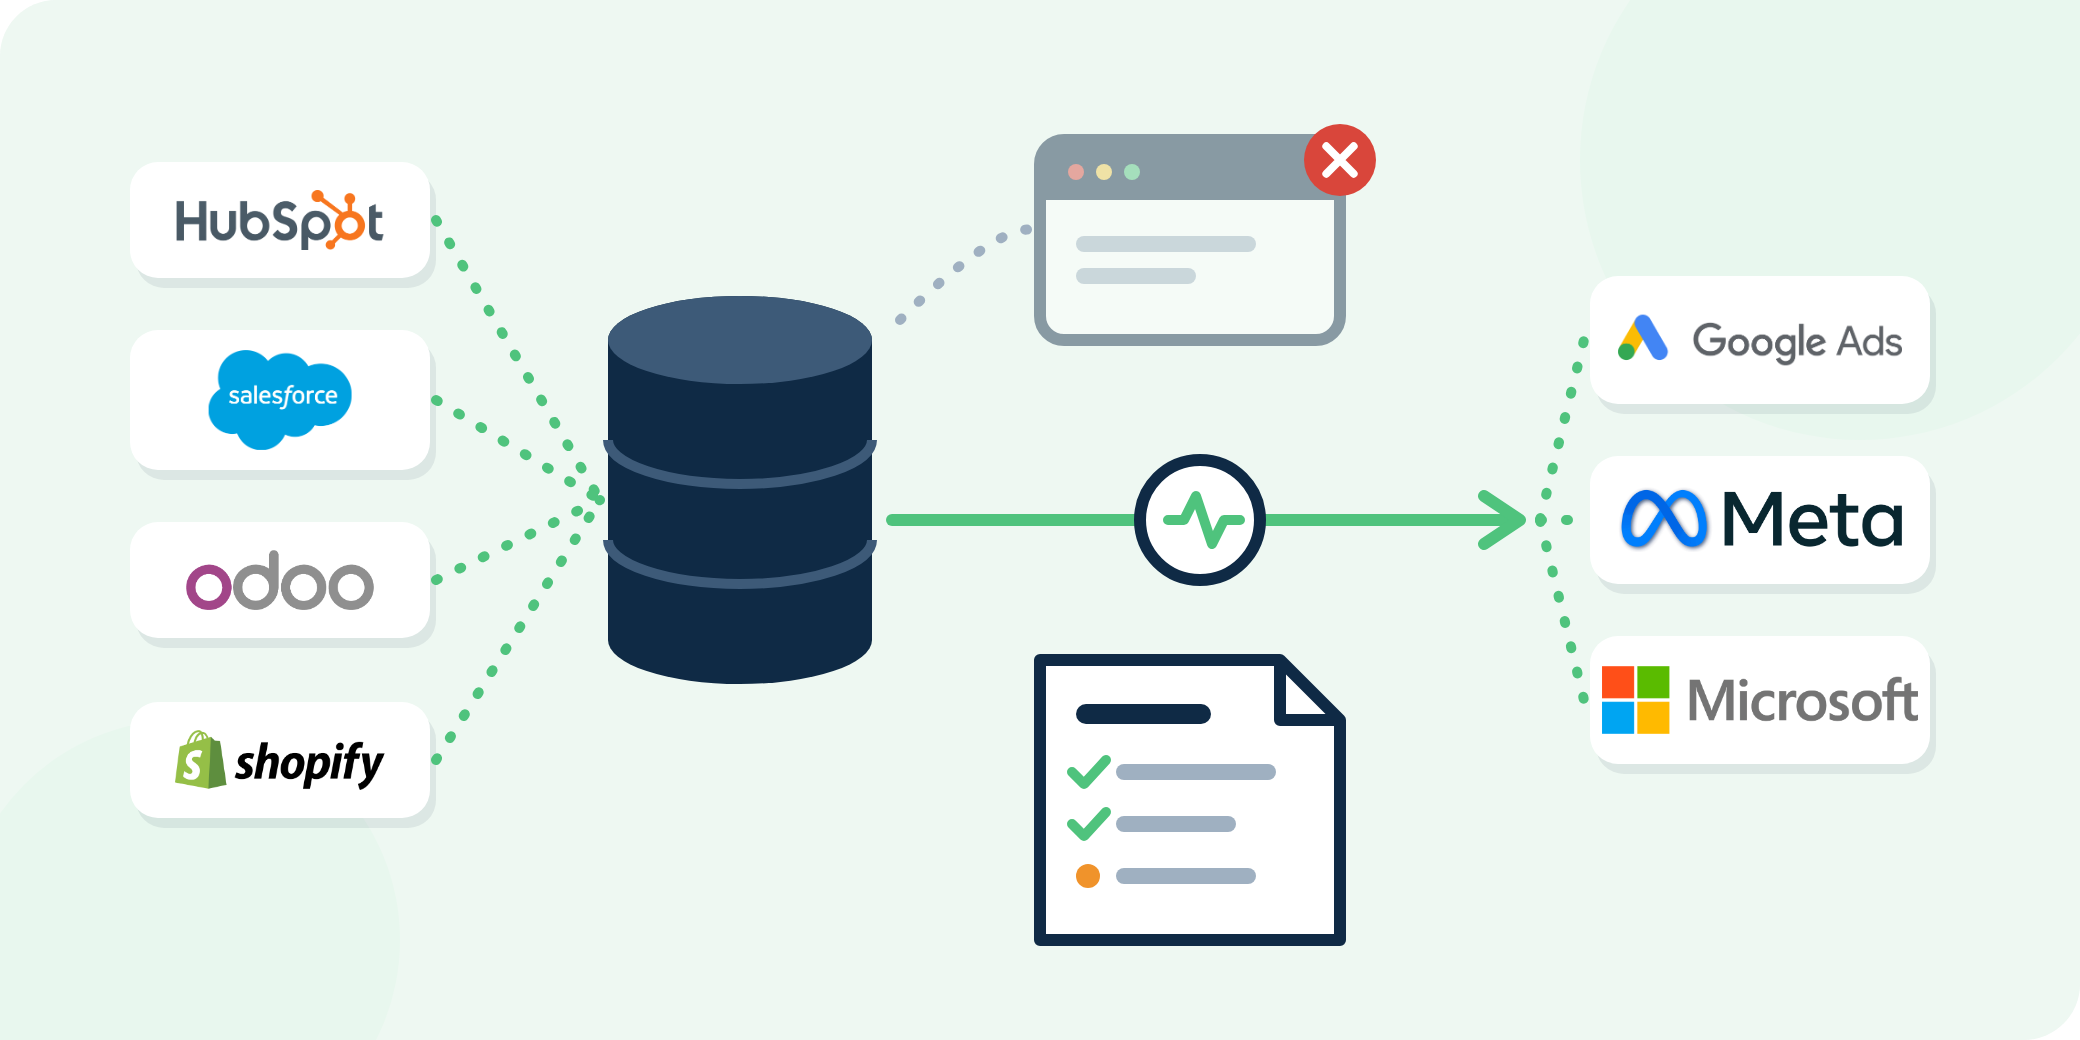
Data sent directly by your CRM, ERP, back office or app, without going through the browser
Offline conversions and real sales sent back to the ad platforms
Matching identifiers (gclid, fbclid, client_id) and consent enforced on the server side
Logging, API errors and flow monitoring
2. FADP and GDPR compliance audit
The Swiss Federal Act on Data Protection (FADP) and the EU General Data Protection Regulation (GDPR) do not require exactly the same things. A website that serves both markets must nevertheless comply with both. Our compliance audit compares what your website actually does with what your legal notices say.
FADP compliance audit
Duty to inform: a complete and up-to-date privacy notice
Data transfers abroad, especially to the United States, and processors
Non-essential cookies and trackers, right to object and banner settings
Technical measures: data minimisation, security and retention periods
GDPR compliance audit
Prior consent: no marketing tag before the user has made a choice
Consent management platform (CMP) and Google Consent Mode v2
Actual cookies, purposes and durations compared with your published policy
Proof of consent and documentation for a regulatory inspection
Our audit is technical: it documents gaps and risks, with evidence. For legal interpretation, we work with partner law firms.
3. Data governance audit
Over the years, agencies come and go, tools pile up and access gets lost. The data governance audit restores order: who collects what, where the data goes and who has access to it.
Data flow mapping: domains, subdomains, tags, tools and recipients
Shadow IT detection: tools installed without approval, orphan accounts and obsolete scripts
Review of access to Google Tag Manager, GA4, Google Ads, Meta and your other platforms
Naming conventions, documentation and division of roles between teams and service providers
How an audit works
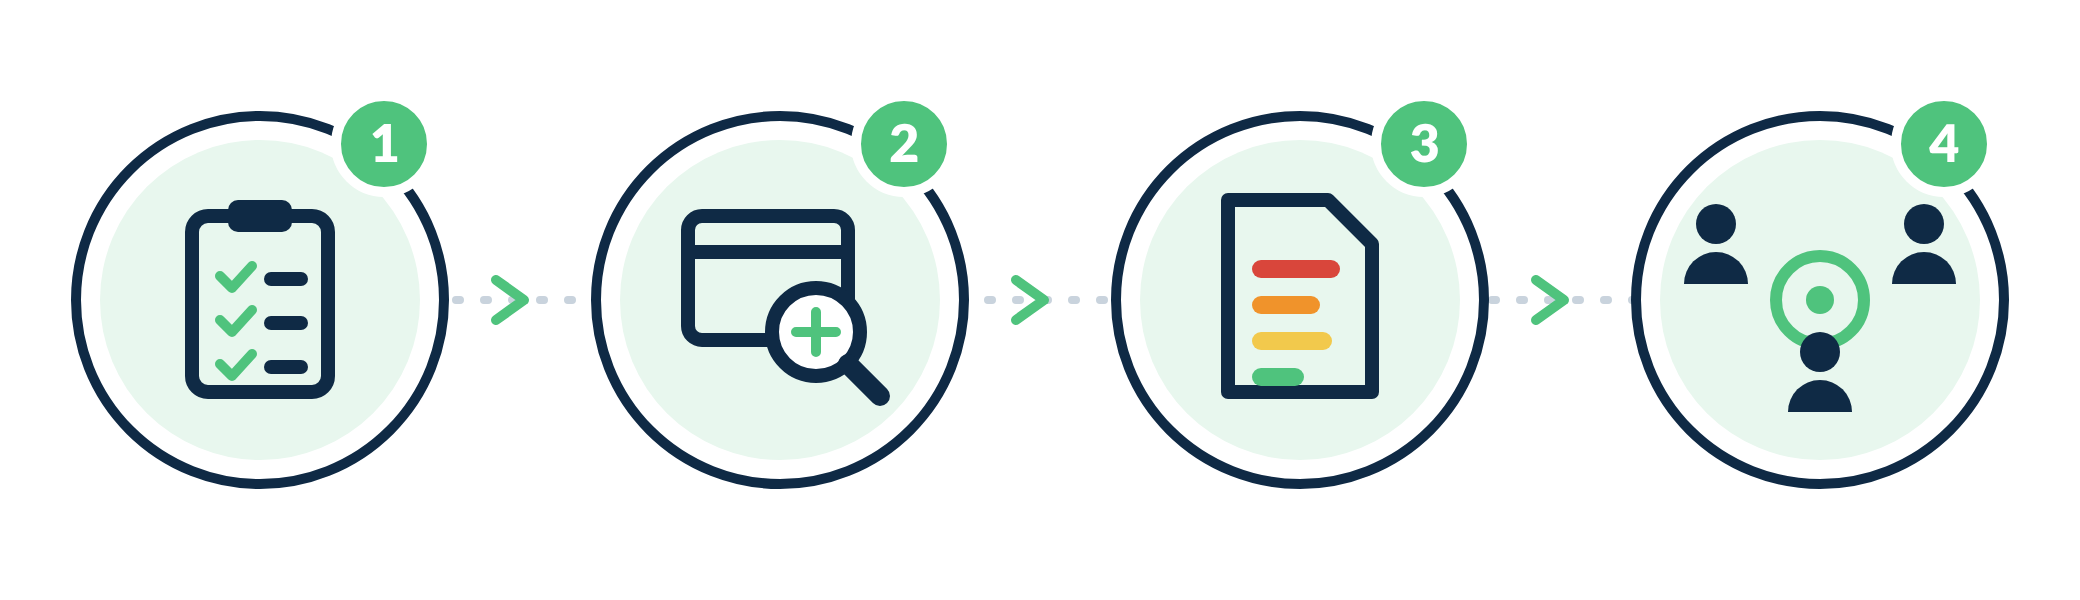
Scoping: your goals, tools and scope (websites, apps, countries), through our technical questionnaire.
Inspection: analysis under real conditions, completed if needed with read-only access to your tools.
Report: findings ranked by risk level (legal, data loss, optimisation), with evidence.
Debrief: a workshop to prioritise fixes with your teams, your agency or your IT department.
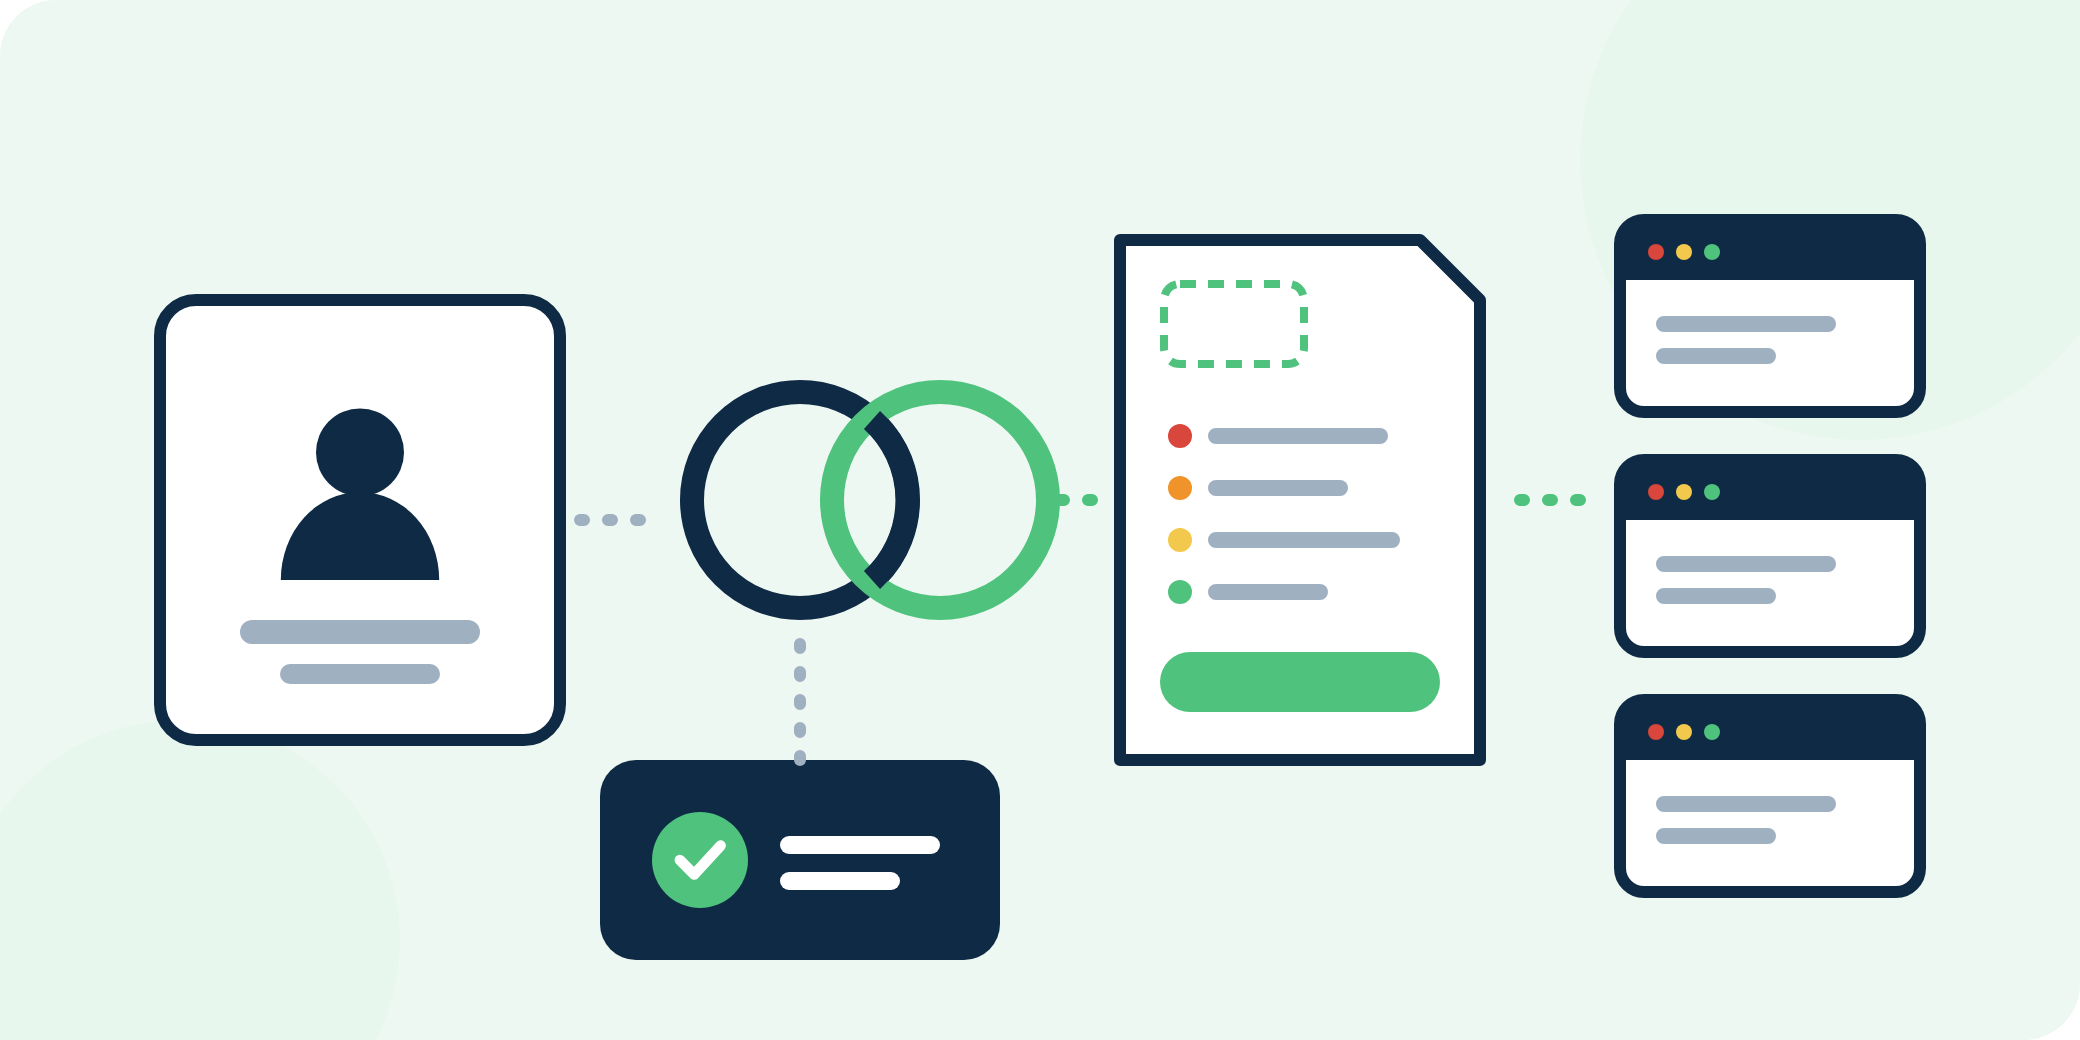
Anonymised extract from an A-Track audit report: each finding is ranked by risk level and backed by evidence.
Who is it for?
Web and marketing agencies
Taking over an account, launching campaigns or rebuilding a website: before you take on that responsibility, you need to know what is really installed. Our audit gives you a factual baseline to present to your client.
Full inventory of inherited tags, pixels and Google Tag Manager containers
Measurement gaps documented before your campaigns inherit them
A report you can share with your client and their developers
SMEs and e-commerce
Your campaigns are expensive and your tools don't show the same numbers. The audit checks that every sale is measured once, with the right value, and that your website complies with the FADP and the GDPR before an inspection or a complaint.
Reliable campaign ROI: sales, leads and basket values
Compliant cookie banner and Consent Mode v2
Prioritised remediation plan for your agency or IT team
Small businesses and freelancers
No data team and no time to waste: you want to know whether your website is compliant and whether your ads are measured correctly. The flash audit gives you the answer within 48 hours, free of charge.
Tags firing before consent
Cookie banner and privacy notice checked
Google Ads and Meta conversions verified
Partners
Agencies, integrators, law firms or consultants: add our audits to your own offering, white-label if needed, and join the partners who already work with us.
Reports delivered in your branding or co-signed
Server-side and FADP / GDPR expertise without hiring
One technical contact for your clients in Switzerland and across Europe
Large organisations
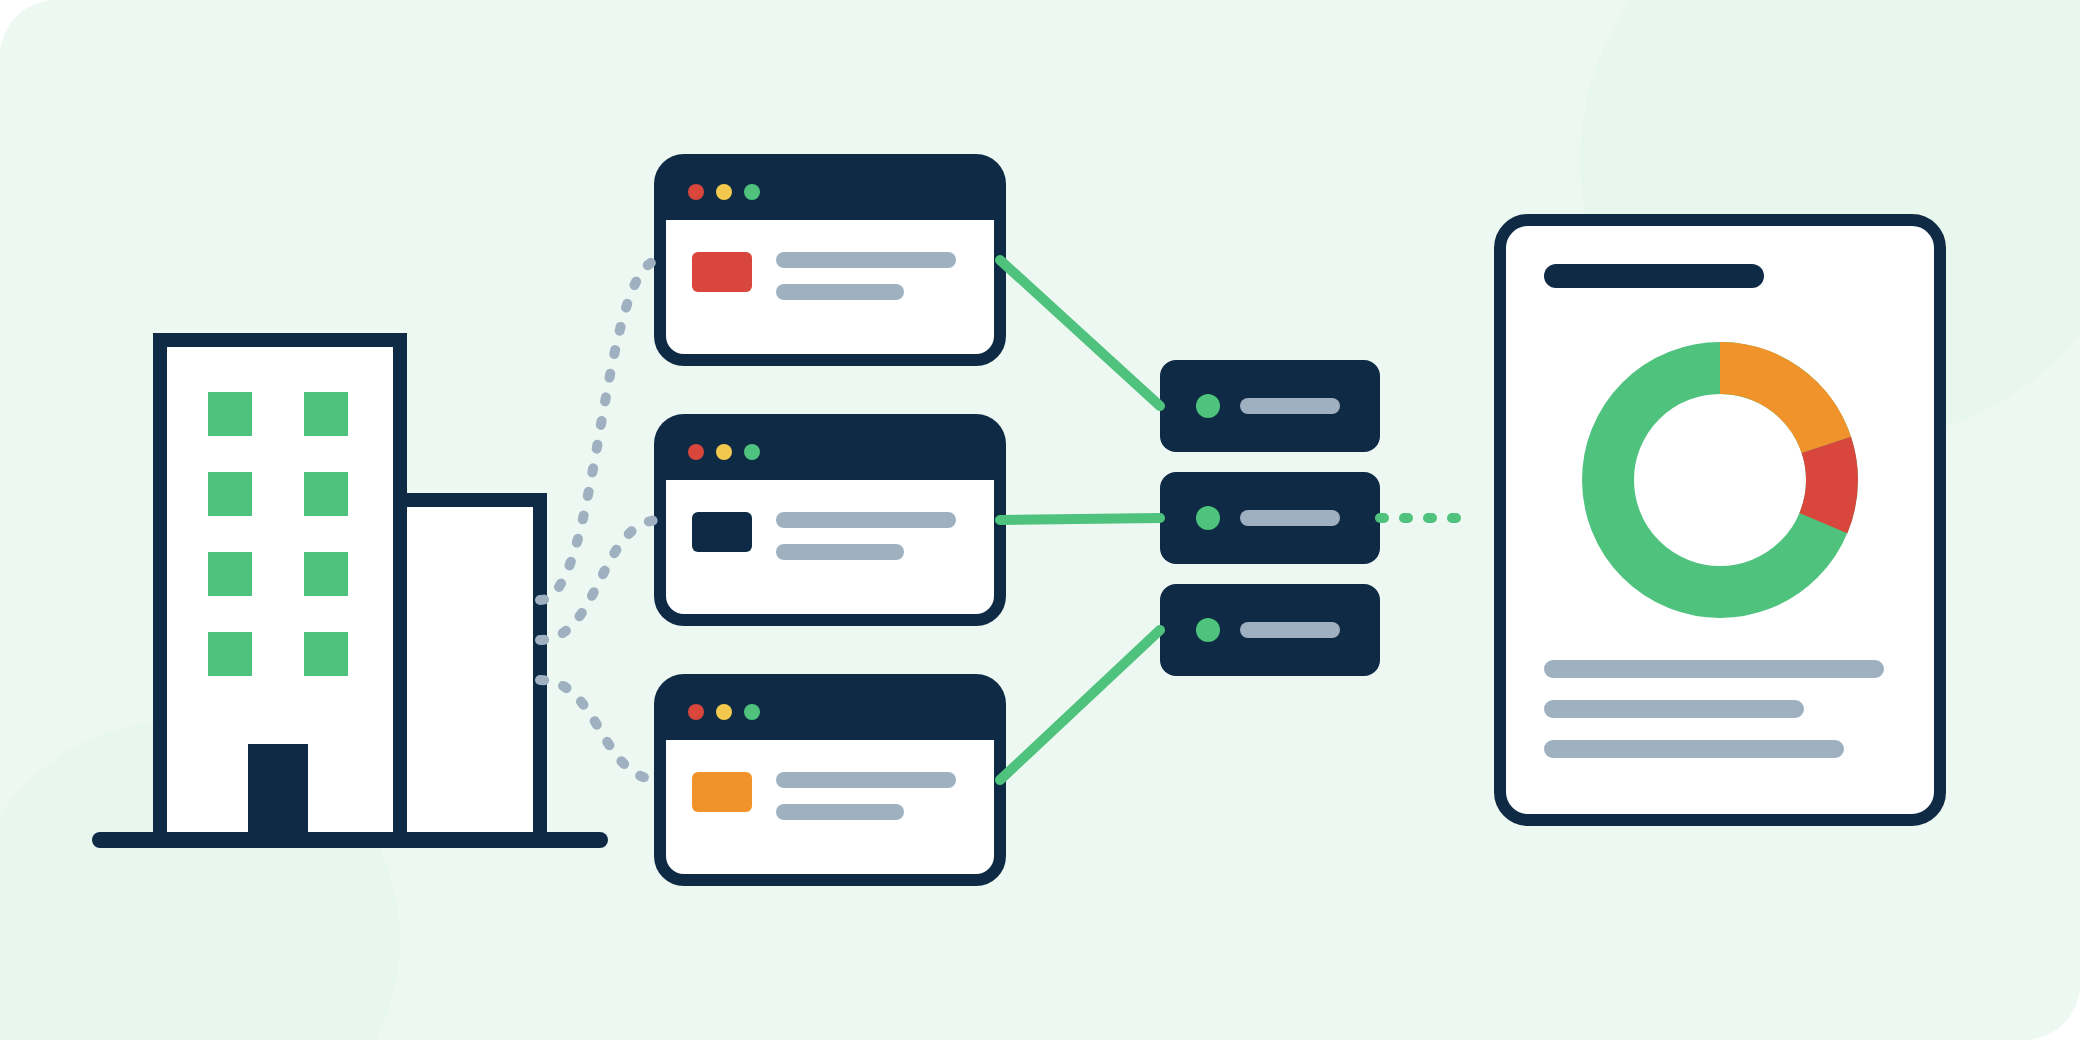
Several websites, several countries, several agencies: measurement fragments and responsibilities blur. We audit all your environments and deliver a board-level report.
Multi-site, multi-country and cross-domain environments
A report for IT, marketing and the data protection officer
Remediation roadmap prioritised by risk level
Pricing: a free audit to start, then a custom quote
We start with a free flash audit within 48 hours of your main website: tags firing before consent, cookie banner, Consent Mode v2 and the first measurement gaps.
Full audits are priced to your needs, based on the number of websites, apps, countries and server-side flows. Fill in our technical questionnaire and we will send you a tailored quote.
Questions fréquemment posées
What is the difference between audit and consulting?
▾
Can we host Google Tag Manager Server-Side at Infomaniak?
▾
This option greatly reduces exposure to foreign law such as the US CLOUD Act, which can appeal to organisations with strict confidentiality requirements (banking, healthcare, public sector). It does, however, mean heavier technical operations (image updates, availability, monitoring). The choice should be made with the company's compliance team.
Can a Swiss bank use Google Ads and Facebook Ads?
▾
On that website, marketing tags fire only after the visitor agrees in the CMP; a refusal is still a refusal. On the server side, A-Track processes data only for statistical purposes and with consent, and filters every request before anything is sent (sensitive parameters and identifiers removed or minimised). The setup should be validated by the bank's compliance team.
How much does a GDPR or FADP audit cost?
▾
For a full audit, our technical questionnaire (https://www.a-track.ch/en/form) lets us send you a precise quote.
What is the difference between a client-side and a server-side tracking audit?
▾
The two complement each other, because most data losses and leaks appear where they meet.
Does a Swiss website have to comply with the GDPR?
▾
Most Swiss websites that also target France or Germany are therefore subject to both the FADP and the GDPR.
How long does an audit take?
▾
The timeline is set during scoping.