Table of content
For years, digital marketing has been waiting for the "end of third-party cookies" in Chrome. It is not going to happen: Google has dropped the plan. Yet your reports keep losing conversions, because Safari, Firefox, ad blockers and consent already restrict tracking. The real question for your clients is no longer "when?" but "how do we measure properly with our own data?".
In short
In April 2025 Google announced it would not remove third-party cookies from Chrome, nor roll out a choice prompt: they stay available.
Safari has blocked them by default since 2020 and Firefox has partitioned them since 2022.
Most Privacy Sandbox APIs (Topics, Protected Audience) were retired in October 2025.
The durable strategy is unchanged: first-party data, server-side and well-managed consent.
Third-party cookies: where do things really stand?
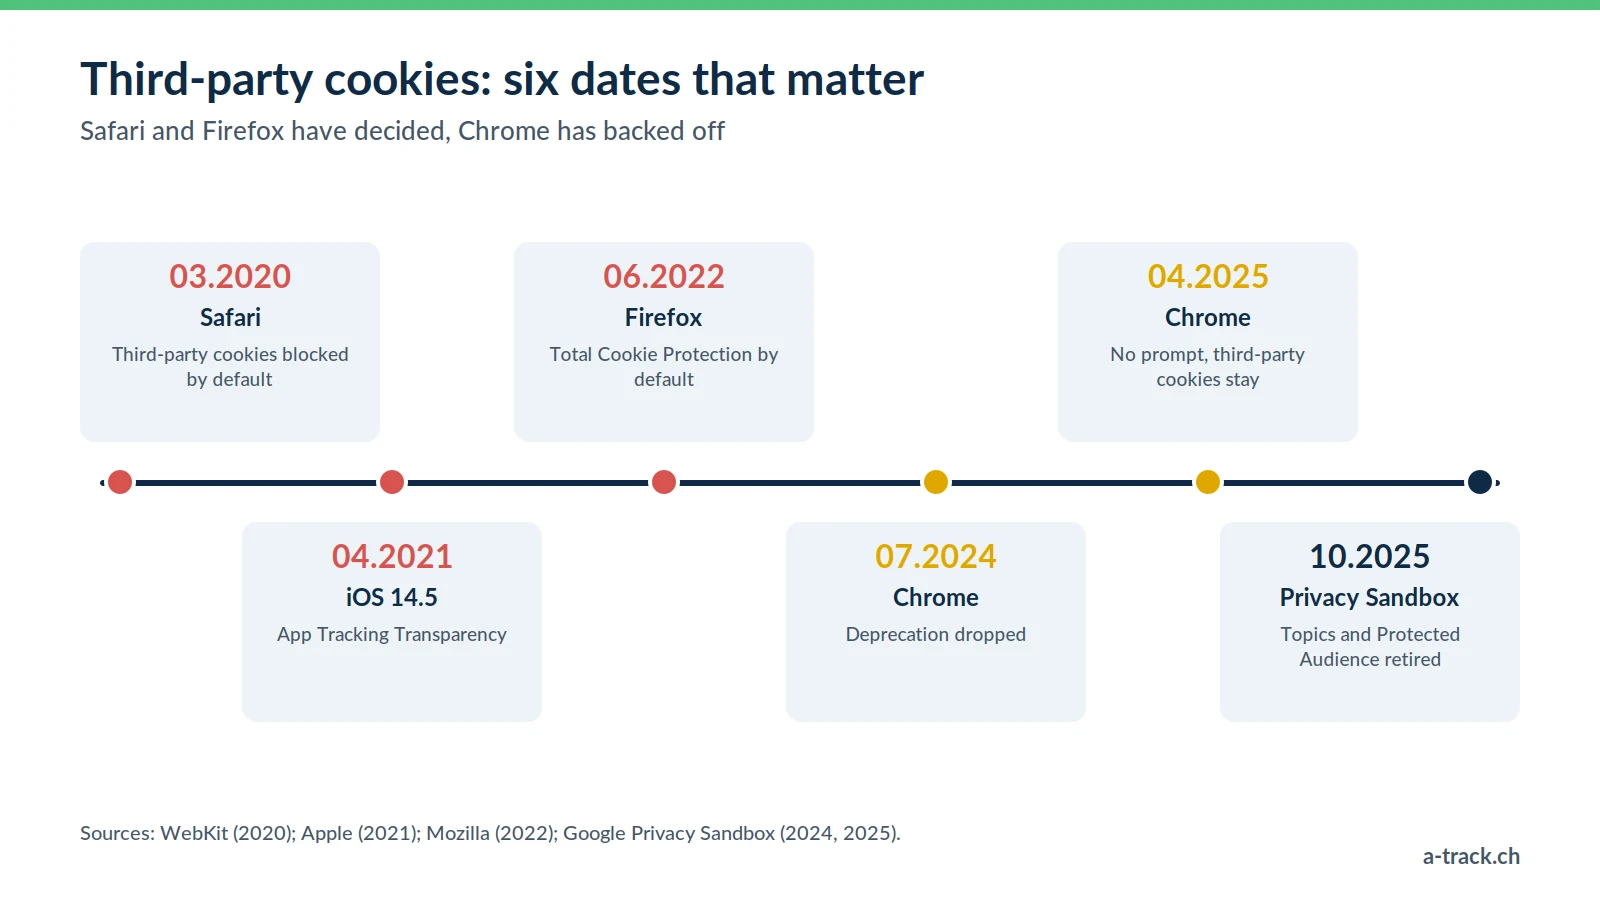
The Chrome saga has had several twists. In July 2024, Google dropped the deprecation in favour of a choice offered to users. In April 2025, it also dropped that prompt: third-party cookies remain managed in Chrome's settings. Finally, in October 2025, Google retired most Privacy Sandbox technologies, including Topics and Protected Audience, citing low adoption.
But Chrome is not the whole web. Safari has blocked third-party cookies by default since March 2020, and Firefox has isolated each site's cookies since 2022 with its Total Cookie Protection. On iOS, App Tracking Transparency has required permission for cross-app tracking since iOS 14.5 (April 2021). For a large share of your visitors, the third-party cookie already no longer works.
Third-party or first-party cookies: a useful reminder
Third-party cookie: set by an external domain (an ad network, a social platform) on your client's site. It is used to follow users from site to site. Status: blocked by Safari, partitioned by Firefox, still accepted by default in Chrome.
First-party cookie: set by the site itself (yourclient.ch) for the cart, language or measurement ID. Status: accepted everywhere, but Safari's ITP caps those set by JavaScript at 7 days.
Your campaigns therefore depend mostly on the quality of your first-party cookies, far more than on the fate of third-party cookies in Chrome.
The concrete impact on your clients' campaigns
Narrower remarketing. Without cross-site tracking on Safari and Firefox, audiences built on third-party cookies shrink.
Weaker attribution. When the measurement cookie expires before the purchase, the sale is credited to direct traffic or brand search, and the campaign that triggered it looks less profitable.
Less precise frequency capping. Without a stable identifier, the same person may see the same ad too often.
The winning strategy: take back control of first-party data
The answer is not a miracle tool but an architecture: owning your data, with the visitor's consent.
1. Reliable first-party measurement (server-side)
With server-side tracking, measurement cookies are set by a server on a subdomain of the site (data.yourclient.ch). They stand up better to browser restrictions, provided the hosting is set up correctly. Details in our article what is server-side tracking.
2. Declared data, with consent
When visitors share an email or phone number (order, form, newsletter), these stable identifiers can be sent in hashed form through Google's enhanced conversions and the conversion APIs (CAPI) of Meta or LinkedIn. This requires clear information and, depending on the market, consent. The agency of tomorrow helps its client collect this data honestly: useful content, newsletter, customer account.
3. Privacy Sandbox: a closed path
The Topics and Protected Audience APIs of the Privacy Sandbox, presented as the alternative to third-party cookies, have been retired. Do not make them a pillar of your plan: build on what you control.
The Swiss context: an opportunity
Switzerland has a strong privacy culture. The revised FADP has been in force since 1 September 2023, and Art. 45c of the Telecommunications Act requires information about cookies and a right to refuse them. On top of that, Google has required consent for personalised advertising to Swiss visitors since 31 July 2024.
This framework pushes towards cleaner, more robust practices. Agencies that tell their clients "we have structured your first-party measurement so it stays reliable and compliant" gain credibility. For the full framework, see our FADP and GDPR compliance guide.
A-Track tip
Do not wait for another Chrome episode. Safari already accounts for close to half of mobile browsing in Switzerland (StatCounter, August 2026): that is where your clients lose the most signal today. Start by auditing the real lifetime of your measurement cookies on iPhone.
Conclusion: your first-party roadmap
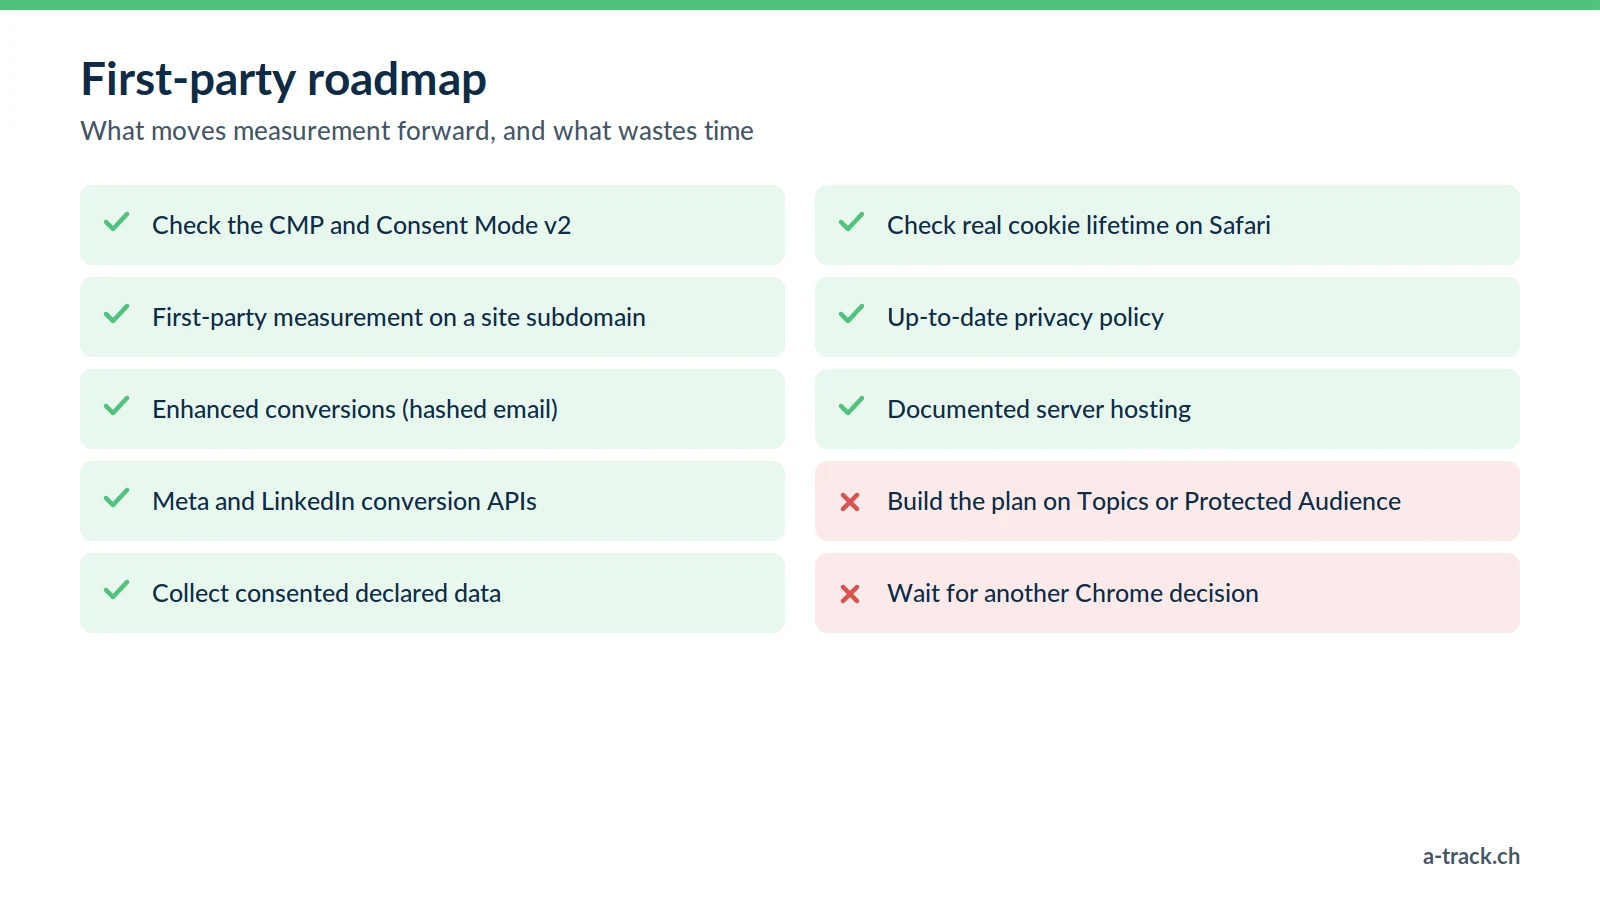
Check the CMP and Consent Mode v2: without a valid consent signal, nothing else works.
Move measurement to first-party (server-side) on a subdomain of the site.
Connect enhanced conversions and conversion APIs (see our Facebook CAPI guide).
Grow the collection of consented declared data, and track the results in your performance measurement strategy.
Does your first-party measurement hold up on iPhone?
A-Track assesses the real lifetime of your measurement cookies, then sets up the CMP, server-side on your subdomain, enhanced conversions and conversion APIs.
Starting point: a free tracking and compliance audit, delivered within 48 hours.