Table of content
When an owner requests an online valuation, they hand over their name, their address and their intention to sell. If that information flows to advertising platforms, the agency takes a legal risk and damages the trust its business depends on. That is what the audit of Bordier-Schmidhauser's website revealed, and what A-Track fixed.
In short
The client: Bordier-Schmidhauser, a Geneva real estate agency (sales, valuation, property management).
The problem: valuation form fields sent to advertising platforms, and tags firing before visitors made any choice.
The solution: server-side tracking that filters data, a CMP and Consent Mode v2 in advanced mode.
The result: no more personal data sent in clear text to ad platforms, and more reliable Google Ads attribution.
Geneva real estate: data that is confidential by nature
A valuation request contains the owner's identity, the property address, its value and a plan to sell. This is personal data under the FADP, and information clients expect to be handled discreetly.
For Bordier-Schmidhauser, trust is the foundation of the client relationship. Yet two behaviours complicate marketing measurement in this kind of sector:
Some visitors refuse cookies, which is their right.
A large share of traffic arrives on Safari or Firefox, whose protections limit tracking (ITP, ETP).
The diagnosis: forms that said too much
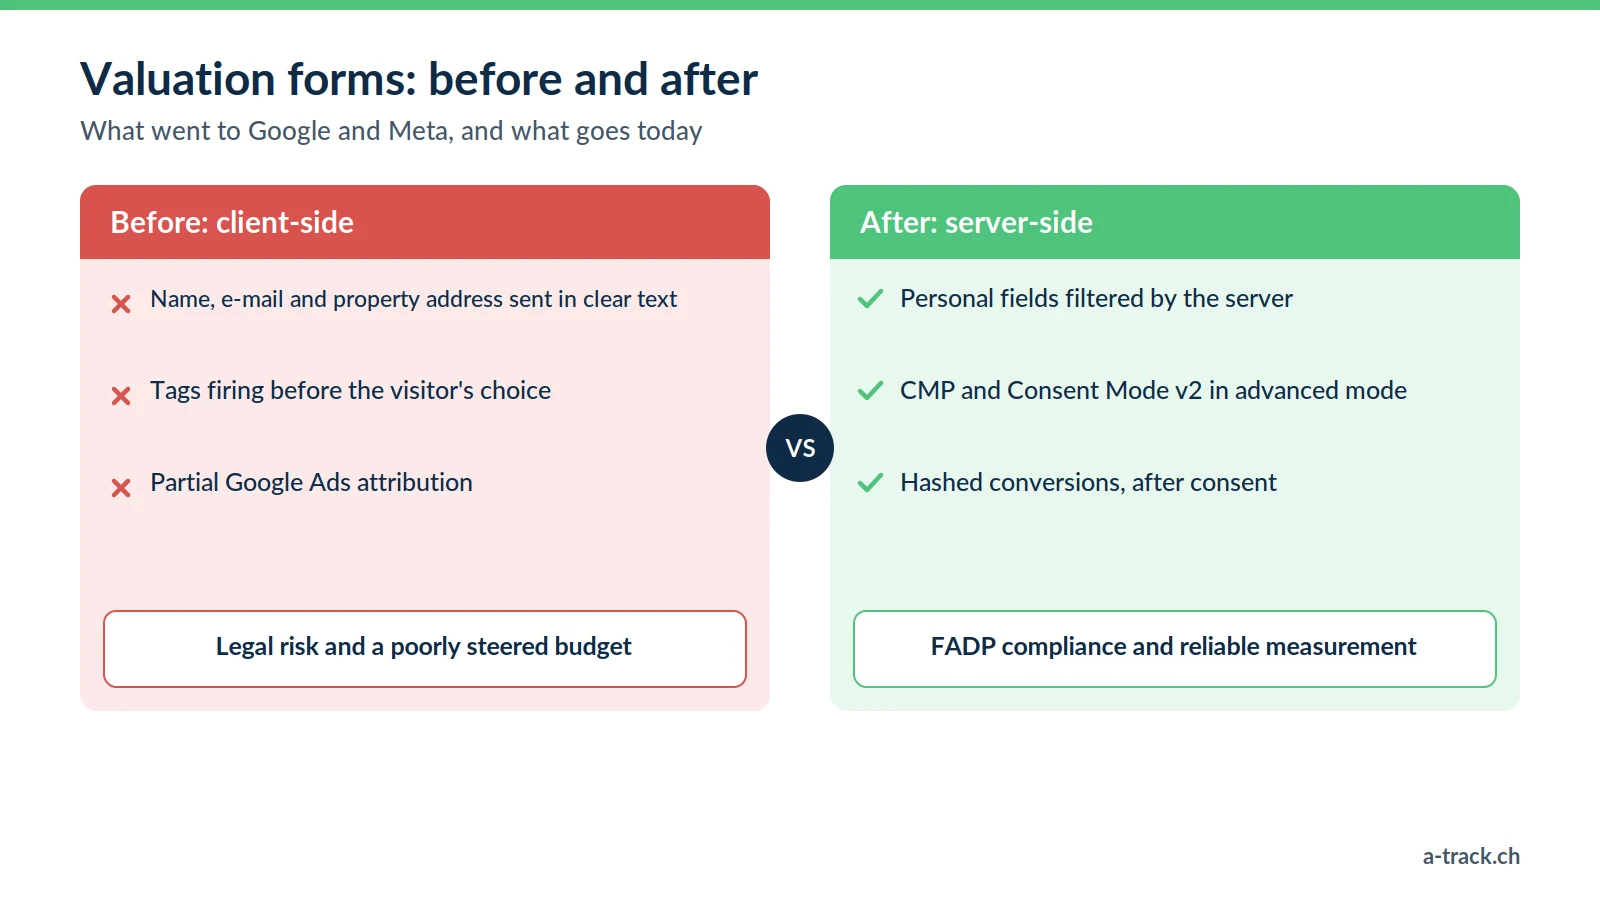
The initial audit uncovered a problem more serious than lost performance. The legacy client-side setup was leaking information:
Valuation form fields (name, e-mail, property address) were captured by tags and sent in clear text to Google and Meta. Google forbids sending it data that can identify a person (Google Analytics PII rules).
Tags fired before visitors made any choice. In Switzerland, the Telecommunications Act (Art. 45c) requires information and a right to refuse; for EU prospects, the GDPR and the ePrivacy Directive require prior consent. And since 31 July 2024, Google has applied its EU user consent policy to Swiss data.
Without reliable measurement, Google Ads campaigns were flying blind on part of the traffic.
The double risk: legal exposure (disclosure of data to foreign platforms without adequate information, under Art. 16 and 19 FADP), plus a poorly steered advertising budget.
The solution: a "privacy-first" server-side architecture
A-Track deployed a server-side tracking architecture on one of the agency's subdomains, designed for compliance first and performance second.
A filtering gateway
All data passes through an intermediate collection server before anything is sent to platforms:
Removal of personal data: name, property address and other fields are never sent to ad platforms.
Anonymisation: IP addresses are truncated before transmission.
CMP and Consent Mode v2 in advanced mode
A CMP was configured and connected to Google Consent Mode v2. When a visitor refuses, no cookie is set: Google only receives cookieless signals and models the missing conversions. According to Google (2021), this modelling recovers more than 70% of click-to-conversion journeys lost to refusals.
Enhanced conversions, after consent
Data sent to Google Ads and Meta (CAPI) is sent in hashed form and only after consent. Hashed data is still pseudonymised personal data, so it is covered in the privacy policy.
A-Track tip: test your forms with the browser's Network tab open. If your e-mail or address appears in clear text in a request to Google or Meta, you have the same problem that was fixed here.
The results: compliance first, reliable measurement next
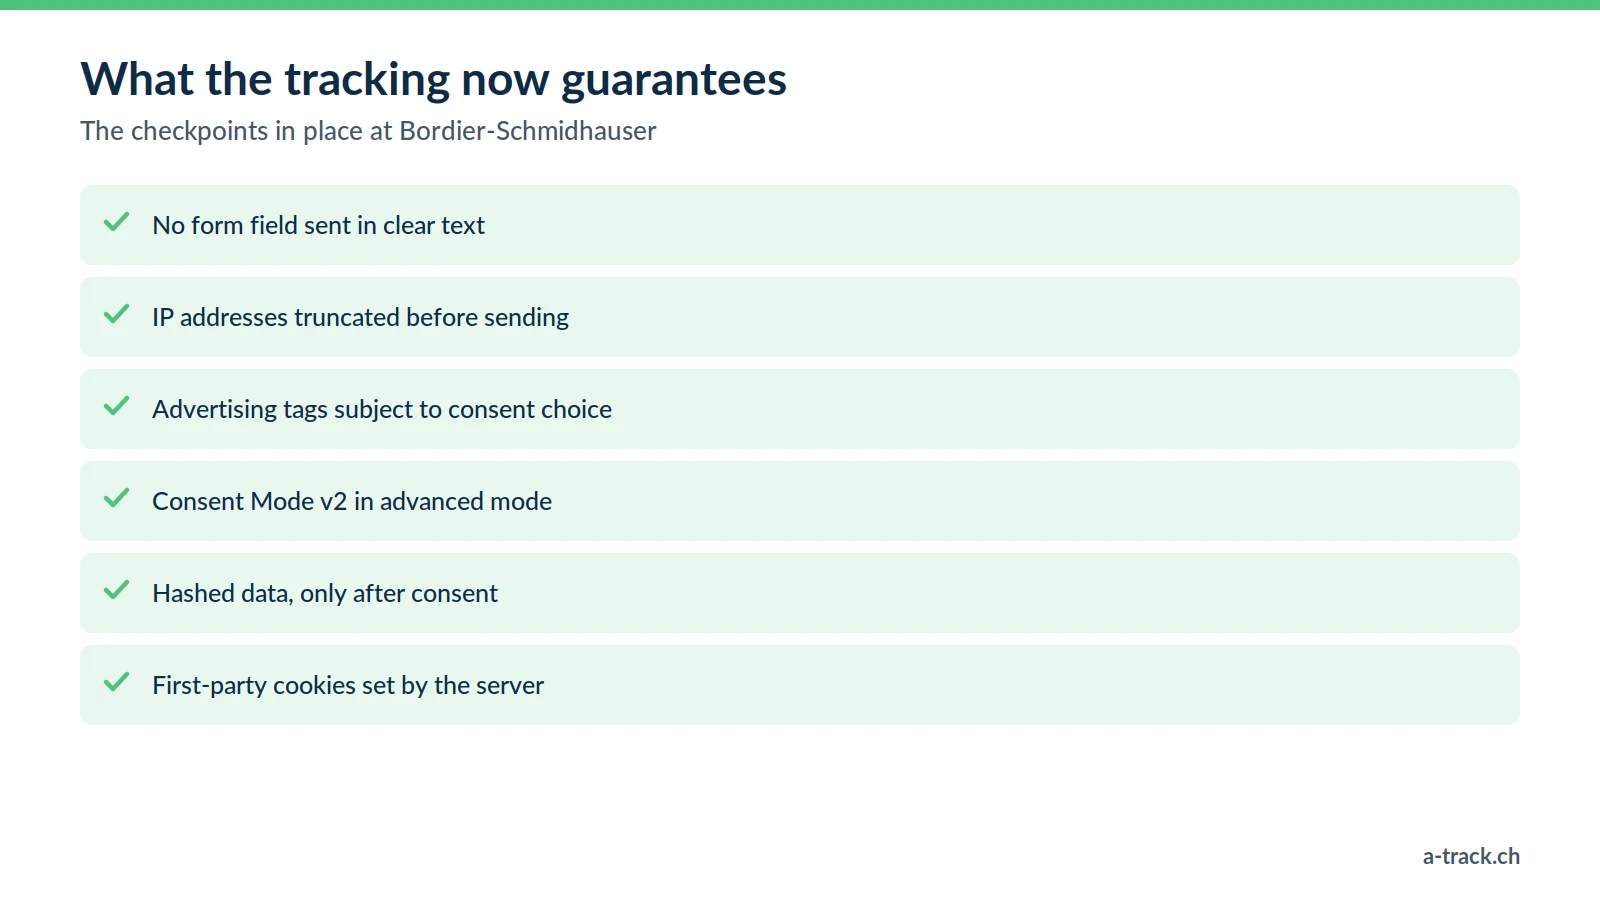
The project shows that compliance is not a brake but a foundation that makes marketing reliable.
Compliance: no more personal data in clear text to platforms. Tracking respects visitors' choices, and documentation is ready if the FDPIC investigates.
Reliability: previously invisible conversions are measured or modelled again, and valuation requests are better linked to campaigns.
Steering: the Google Ads algorithm is fed cleaner, more complete data, so it bids on real signals.
For another case with figures in a trust-based sector, read our G. Salerno & Associés case study.
Technical focus: Safari visitors (ITP)
Without server-side, Safari visitors' cookies have a shorter life: according to WebKit, 7 days without interaction for cookies created in JavaScript, or even 24 hours after a tracked link.
With first-party cookies set server-side, a valuation request can be linked to a first visit made several weeks earlier. A decisive advantage when the decision to sell a property takes months.
Conclusion: compliance as a competitive advantage
In a sector where trust is the main asset, FADP compliance is not a brake, it is a selling point. Three checks to run on your website:
No form field should be sent in clear text to an ad platform.
No advertising tag should fire before the visitor has chosen.
Your measurement server should filter what leaves it, with documented rules.
Our FADP and GDPR compliance guide covers each step.